Security
Follow a launch
Following pins that title's stories to the top of the feed and puts its countdown here. It never hides anything.
Muted sources
Nothing muted. Every card carries a mute control in its corner.
This browser is blocking site storage, so these choices last until the tab closes.



France blames Iranian hackers for supermarket attacks that sparked fires
France has linked October cyberattacks that disrupted refrigeration systems at more than 700 supermarkets and other retail locations to Iranian…
Russian cloud firm Beget rebuilds from scratch after data wiper attack
A data-wiping malware attack has forced Russian cloud services provider Beget to rebuild its cloud infrastructure from scratch, the company said.
Binance denies data breach after alleged ShinyHunters claims
Binance, the world's largest crypto exchange, has denied claims of a new security breach made by a threat actor using the 'ShinyHunters' handle on a…
FBI agent stole $2.5 million in crypto from hackers under investigation
A former FBI agent has pleaded guilty to stealing nearly $2.5 million from the wallets of fraud victims and nation-state hackers under investigation.
US bans MEXC crypto exchange over sanctions evasion, cybercrime links
The US Department of the Treasury has cut off the MEXC Global crypto exchange from the US financial system over sanctions evasion and links with…
Ukraine dismantles crypto scam network that stole €4.3 million
Ukrainian law enforcement arrested four suspects in a case involving the theft of more than €4.3 million using a network of cryptocurrency investment…
Iris Ohyama data cloud breach exposes info of 7.7 million customers
Japanese manufacturer Iris Ohyama, the operator of the Iris Plaza shopping platform, disclosed that personal information belonging to about 7.7…

Hackers Exploit Qubole's Trusted AWS Access to Breach Customer Accounts and Steal Data
An attacker broke into AWS accounts belonging to multiple Qubole customers between October 14 and October 26 and stole stored secrets and data, cloud…

Hackers Compromise Ethersphere's bee-js and Swarm Desktop to Deliver Wallet-Stealing Malware
Attackers used the Ethersphere project's own release automation to publish malicious versions of two of its tools for the Swarm decentralized storage…
Nvidia CEO Jensen Huang under investigation after admitting affair with alleged Chinese spy in company-wide email
Nvidia's board of directors has launched an investigation into its own CEO Jensen Huang, after a report by the New York Times claimed he had been…

Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia
The South Asian cyber espionage group known as Bitter (aka APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed…

⚡ Weekly Recap: SSHole Exploited, APT Root RCE, Robot Takeovers, 15K Hacked Sites, and More
A system doesn't always need a complicated bug to let someone in. Sometimes, a blank password is enough. That's one of the bigger stories this week.

Default 'admin:admin' Server Password Helps Researchers Hack Two Automakers, Unlock and Start Cars
The login systems behind two car brands' mobile apps could be taken over completely, two security researchers found, allowing them to access any…

Web3Auth Flaw Exploited to Steal Keplr Crypto, Provider Empties Other Wallets for Safety
Some people who set up a Keplr crypto wallet with their Google or Apple account have had money stolen by an attacker.

LNbits Urges All Operators to Shut Down Their Bitcoin Lightning Wallet Servers Amid Attacks
Everyone running LNbits, a free, open-source Bitcoin Lightning wallet system, should shut down their servers now because of a wave of attacks, the…

Taiwan-Based Hacker Used BOSSAI AI Agents to Steal Taipei Emergency Dispatch Records
A single attacker using AI agents pulled emergency dispatch records covering seven Taipei districts, researchers at Acronis's Threat Research Unit…

CISA Flags SonicWall SonicOS MFA Bypass Flaw Amid Reports of Possible Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity vulnerability impacting SonicWall SonicOS to its Known…
Hackers pull off $133 million French bank heist via service provider
French cooperative bank Crédit Mutuel Arkéa was targeted in a cyberattack that enabled fraudulent transactions of up to $133 million, forcing it to…
CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands
Scammers are impersonating major brands and celebrities to lure consumers into fake gift card giveaways that collect personal information and trigger…

NVIDIA Launches Investigation Into Jensen Huang's Relationship With Suspected Chinese Spy
NVIDIA announced on Sunday that the company's board of directors is launching a full-scale independent investigation into recent reports of founder…

A new standard for vulnerability management in the AI era
Windows is evolving vulnerability management as advances in AI make it possible to discover and analyze security vulnerabilities faster and at…
Chainalysis says hackers stole credentials and tokens for all of its customers
Company said a "multifront cyberattack" included AI agents and an on-path data snatch.

Want to Rent an Internet Address at the White House?
Several staffers at the White House are using computers or mobile devices equipped with residential proxy services that render their internet address…

Installing the Fix for an Exploited WordPress Flaw Can Expose Some Sites One Last Time
Some WordPress sites can still be attacked while they install the fix for an actively exploited flaw, according to Umut Bayram, the Picus Security…

Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies
Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with…
 Illustration
Cloudflare links vulnerability discovery to defense with OpenAI
Cloudflare uses OpenAI Daybreak to investigate vulnerabilities and propose fixes for review.

Microsoft Paint RCE Fix Now Available, but Windows Update Won't Deliver It
A fix for CVE-2026-83844, a remote code execution flaw in Windows Paint, is now in the Microsoft Store.

The Flood is Coming And The Pipes Were Already Full
An update on Athena, and some unsolicited predictions on what's coming next On Saturday, Dario Amodei published We Must Pace the Frontier.
Linux Fixes Faulty Mitigation Selection For BHI Vulnerability
This week's batch of x86 fixes have been sent out ahead of the Linux 7.4-rc2 kernel releasing later today...
WoW: Forever is the biggest launch in World of Warcraft history, says Blizzard
World of Warcraft: Forever is the biggest launch in the MMO's history, pulling in more concurrent players than any previous WoW launch.

Chainalysis Breach Exposes All Users' Credentials, Forces Shutdown of Key Services
Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed…

Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without Logs
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at…

Experts Demonstrate Barracuda Email Security Gateway Chain Enabling Root Access Without Login
Two flaws in Barracuda's Email Security Gateway, an email-filtering appliance, can be chained to run commands on it as root, its highest level of…

OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine Linux
Attackers can log in to accounts that have no password, such as SSH key-only accounts, on some Alpine Linux servers running the standard…

Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI…

ThreatsDay: Apache OFBiz RCE, DreamHost Breach, DeFi Site Hijacks + 17 More Stories
How much damage can someone do without breaking much? Quite a lot, it seems. A stolen login can open doors across several systems.

Is Your Exposure Management Platform Leaving You Exposed? Five Tests to Find Out
A critical finding can move through several security tools and still leave the organization exposed.

5 Active Cyber Threats That Put US Enterprises at Risk in October 2026
October 2026 brought another wave of cyber threats targeting US businesses, with attackers exploiting trusted platforms, legitimate authentication…

CERT-In Flags AI-Driven Attacks as Backdoored ARTEX Exposes 62 Consoles to Root Access
The Indian Computer Emergency Response Team (CERT-In) has disclosed that an artificial intelligence (AI)-assisted threat actor it tracks as Crafty…
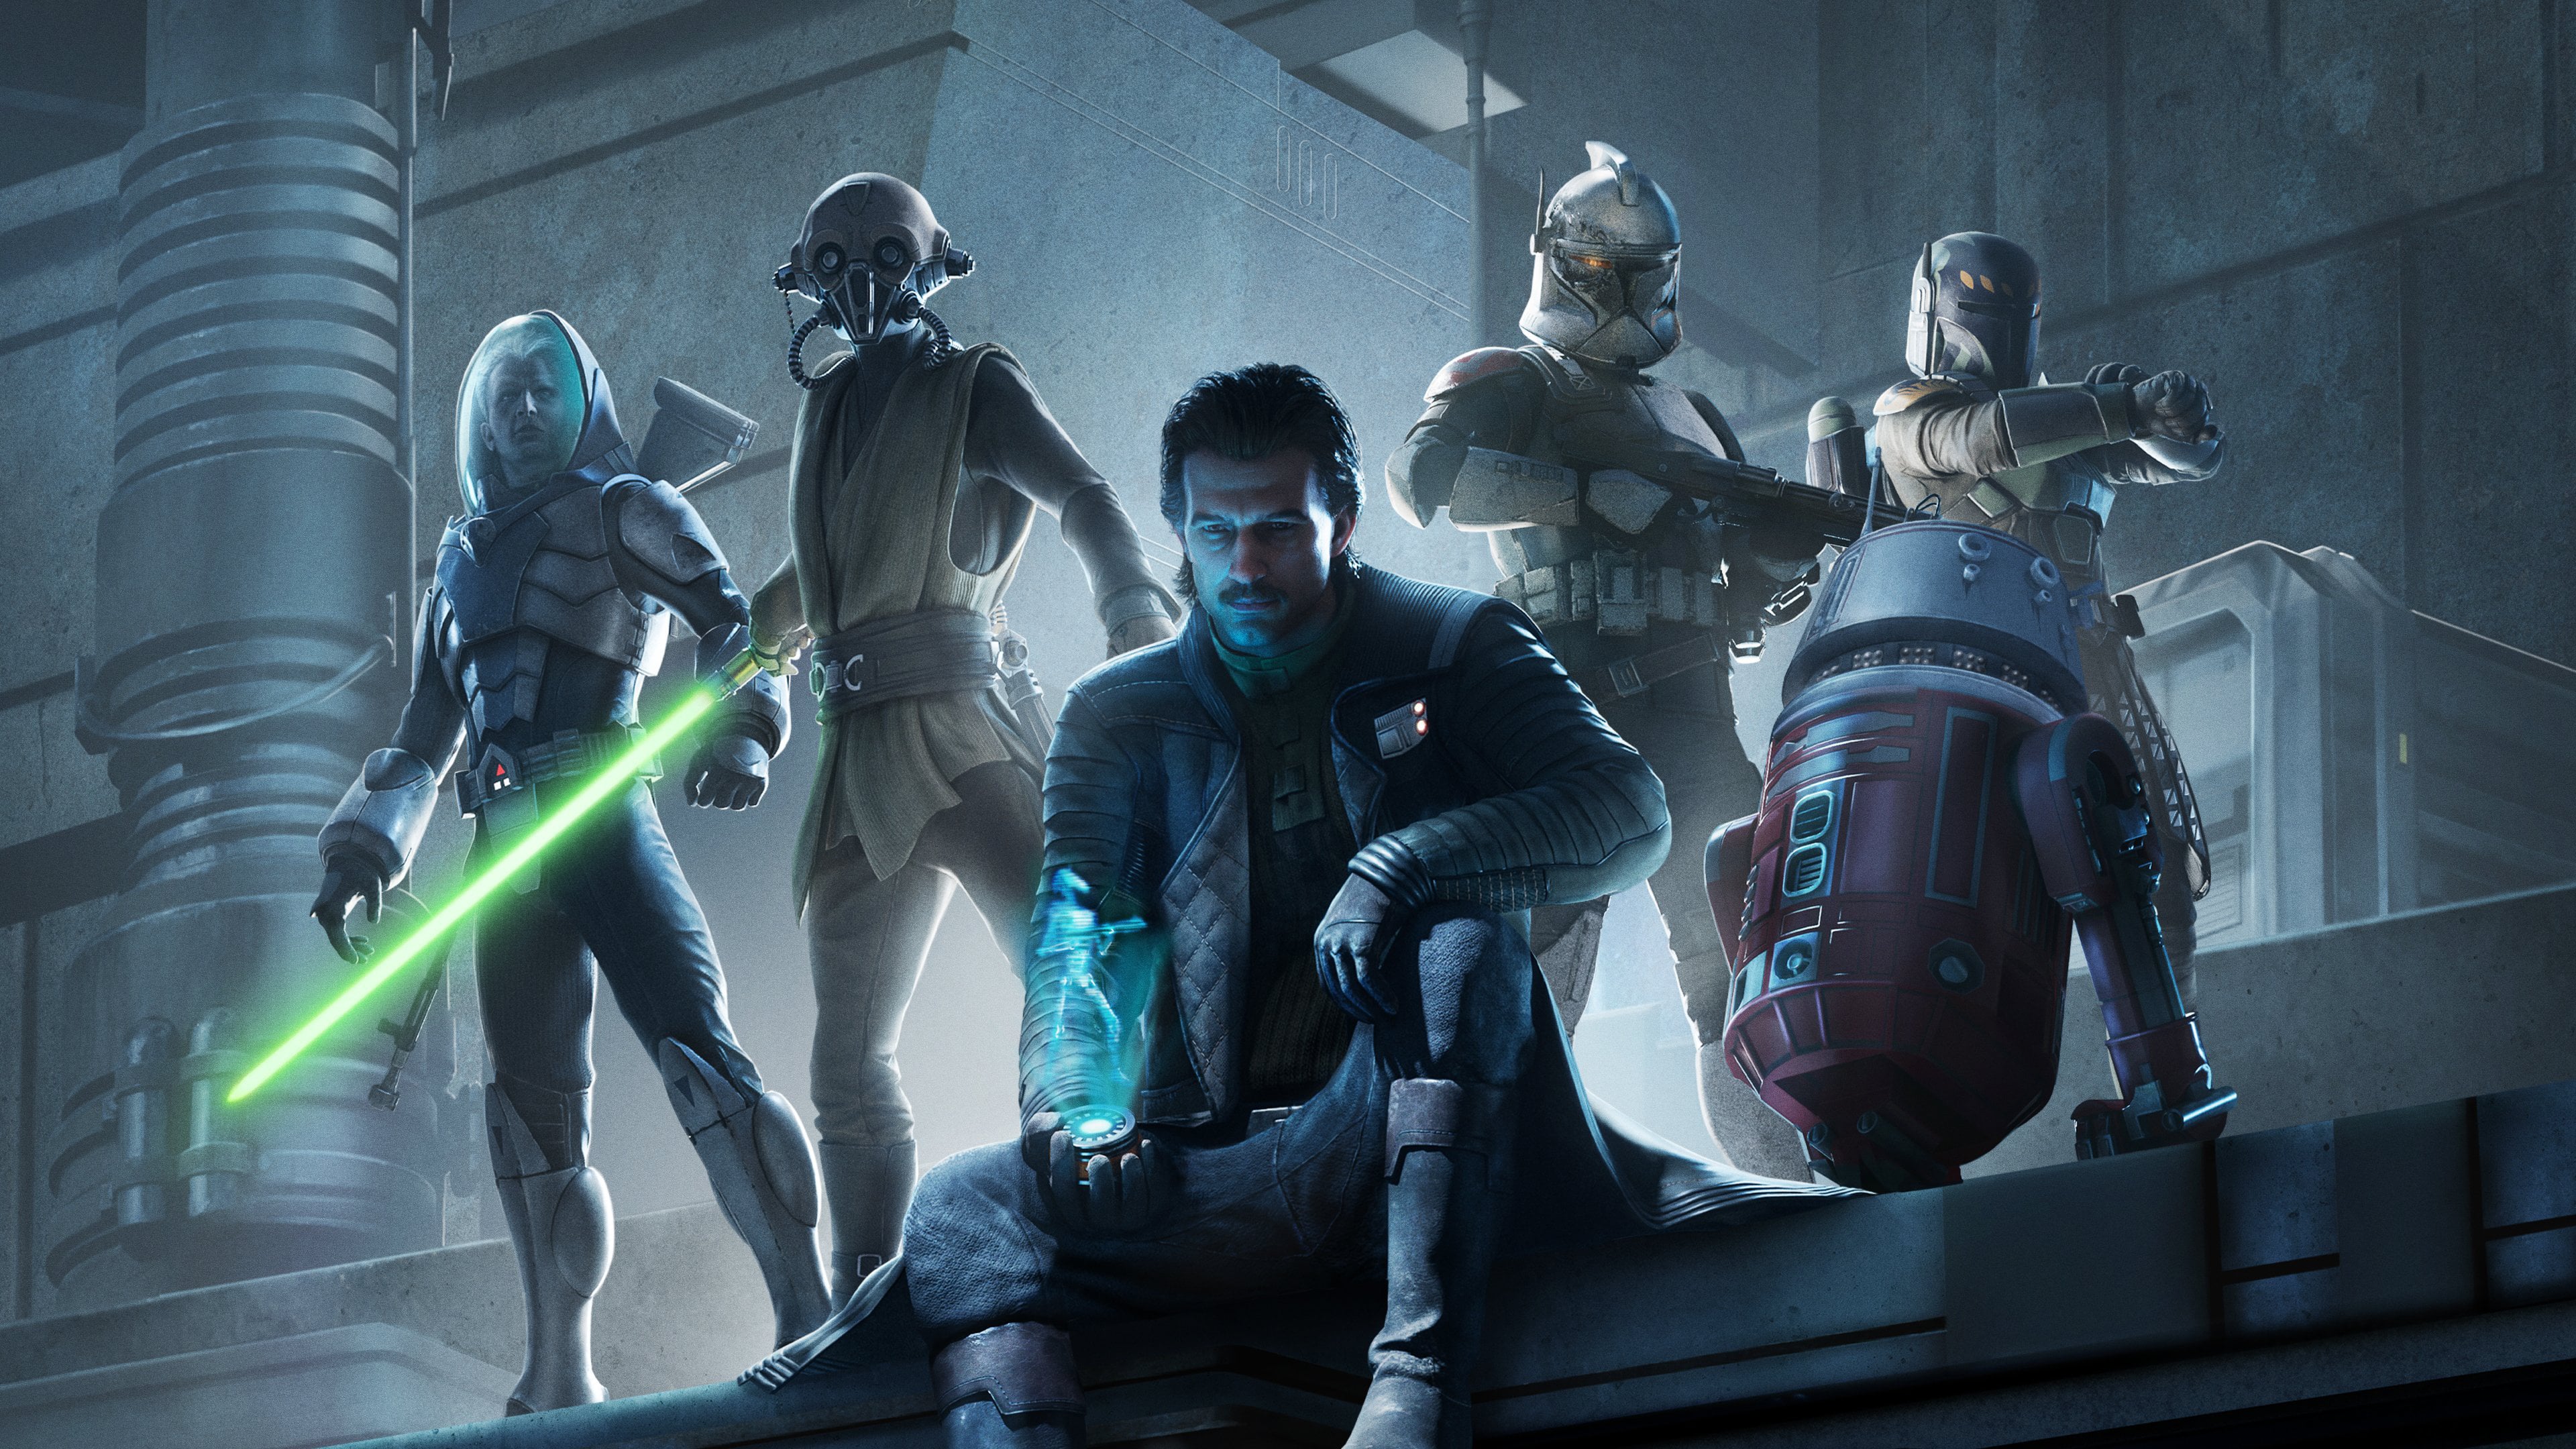
Star Wars Zero Company studio Bit Reactor is laying off staff, a month after it started bringing back furloughed devs
The game sold roughly 1 million copies in its first month and a half

Zyxel GS1900 Patch Fails to Block Zero-Day Exploit Allowing Root Command Execution
Zyxel GS1900 network switches that received the vendor's earlier fix for an actively exploited flaw are still open to the exploit attackers used,…

Debian and Ubuntu APT Flaw Lets MitM Attackers Swap Verified Packages and Run Code as Root
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their…

APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through…

Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads
A critical flaw in Ruby on Rails could allow an unauthenticated attacker to write arbitrary files on an app's server by uploading a crafted file if…

Xen Hypervisor Flaws Let One Malicious VM Read and Write Any Other VM's Memory
Two flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including…

China-Aligned Hackers Hijack Sogou Input Method DNS Requests to Deploy DarkVigil Backdoor
A China-aligned threat actor known as SlippyNunchucks has been attributed to a Domain Name System (DNS) hijacking operation abusing insecure HTTP…
 AnsyahF · GPL · Wikimedia Commons · illustrative
Seven stable kernels with fixes for three Xen vulnerabilities
Hot on the heels of the previous two stable kernels, Greg Kroah-Hartman has announced the release of the 7.3.3, 6.18.62, 6.12.116, 6.6.162, 6.1.192,…

Russian Police Arrest 3 Suspected VasyGrek Hackers, Dismantle Criminal Infrastructure
Russian authorities have arrested three suspected members of a threat group known as VasyGrek and dismantled its criminal infrastructure.

CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities…
OpenIndiana 2026.10 released
Version 2026.10 of the OpenIndiana operating system has been released. OpenIndiana is based on Illumos, which in turn was based on OpenSolaris after…

Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
U.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives…

U.K. Sanctions Cryptomus for RU Money Laundering
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit…

mSecure Warns Users to Change Passwords, Reset 2FA and Passkeys After Suspicious Activity
Customers of the mSecure password manager are being urged to act now to protect the confidential information they store in it, possibly by changing…

Chainstack Reports Production Systems Breach Exposing Customer Data and Password Hashes
Blockchain infrastructure provider Chainstack on Tuesday disclosed that it was targeted in a cyber attack that allowed an unauthorized party to gain…

Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a…

Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access
Barracuda has disclosed details of two vulnerabilities affecting its products that, if chained together, could allow an attacker to bypass…

cPGuard Update Channel Hijacked to Backdoor Linux Servers and Collect Password Hashes
An attacker broke into the update system of the cPGuard security tool on November 2 and used it to send a malicious script to customers' Linux…

Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing
Fixed kernels for a use-after-free vulnerability in the Linux kernel's IPv4 TCP code are now available for Red Hat Enterprise Linux 8, 9, and 10,…
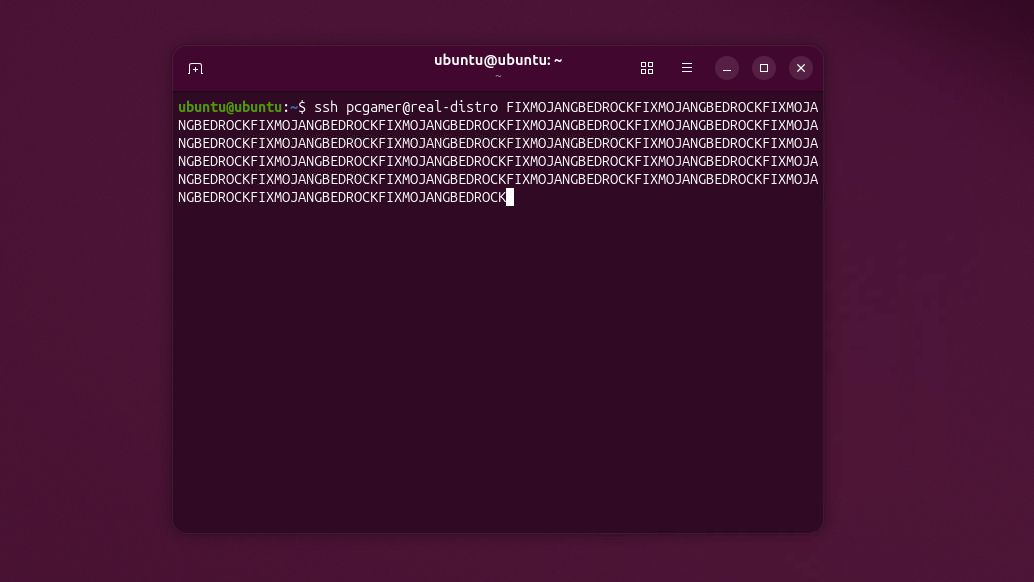
All that stands between a hacker and admin privileges on some Linux distros is a 257-character long string of literally anything
Eeeeeeeeeeeeeep. Thankfully there's already a fix out.
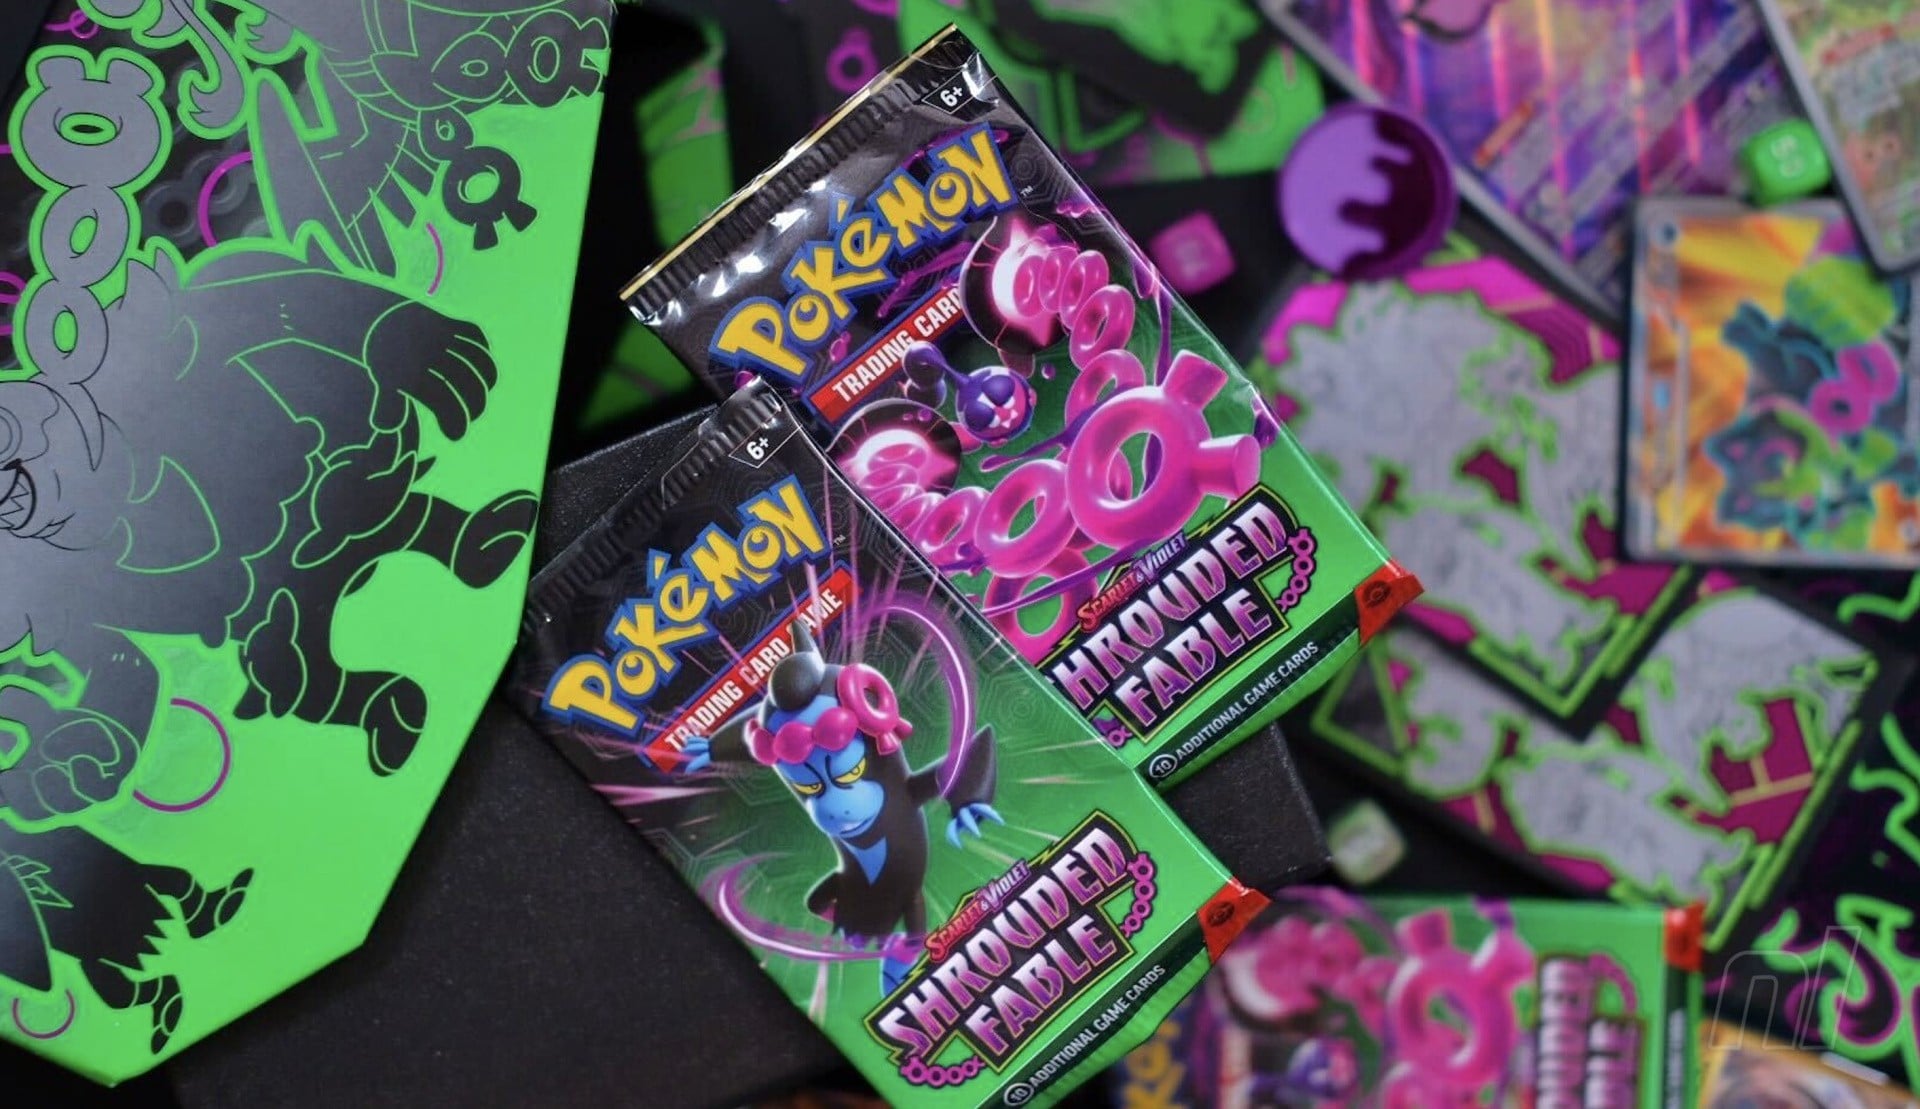
Father Arrested For Leaving 6-Year-Old Daughter Sleeping In Line For Pokémon Cards
NL used Rage. A 35-year-old South Carolina man has been arrested and accused of leaving his 6-year-old daughter asleep while waiting in line for…